
View benchmark rules
Review the individual rule results within a benchmark that ran as part of a scan.
Procedure
-
In the top navigation bar, select
 > Compliance.
The Compliance page opens.
- Select the Scan logs tab.
- Select the applicable scan.
-
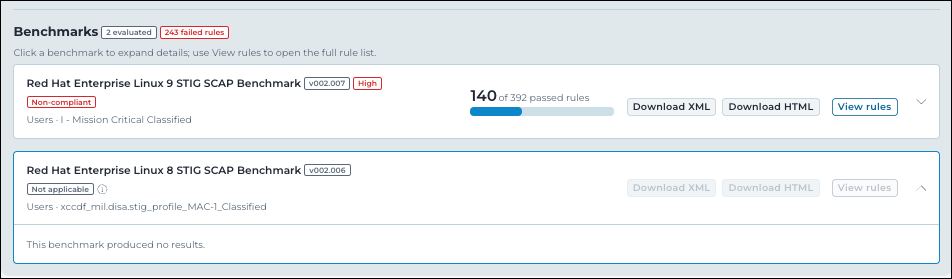
Select the applicable benchmark to expand its details, then select
View rules.
If the benchmark produced no results, for example because its status is Not applicable and it does not apply to the operating system (OS) family of the host it ran against, the expanded panel shows This benchmark produced no results. instead of rule counts and timestamps.
-
Select the applicable rule to expand its details.
 Along with its rule identifier (ID) and override status, the
rule detail panel shows:
- Description: Background information about what the rule checks and why it matters
- Remediation: The recommended action to bring the host into compliance with the rule
- Evidence: The technical scan output used to evaluate the rule, including the specific test results
Results
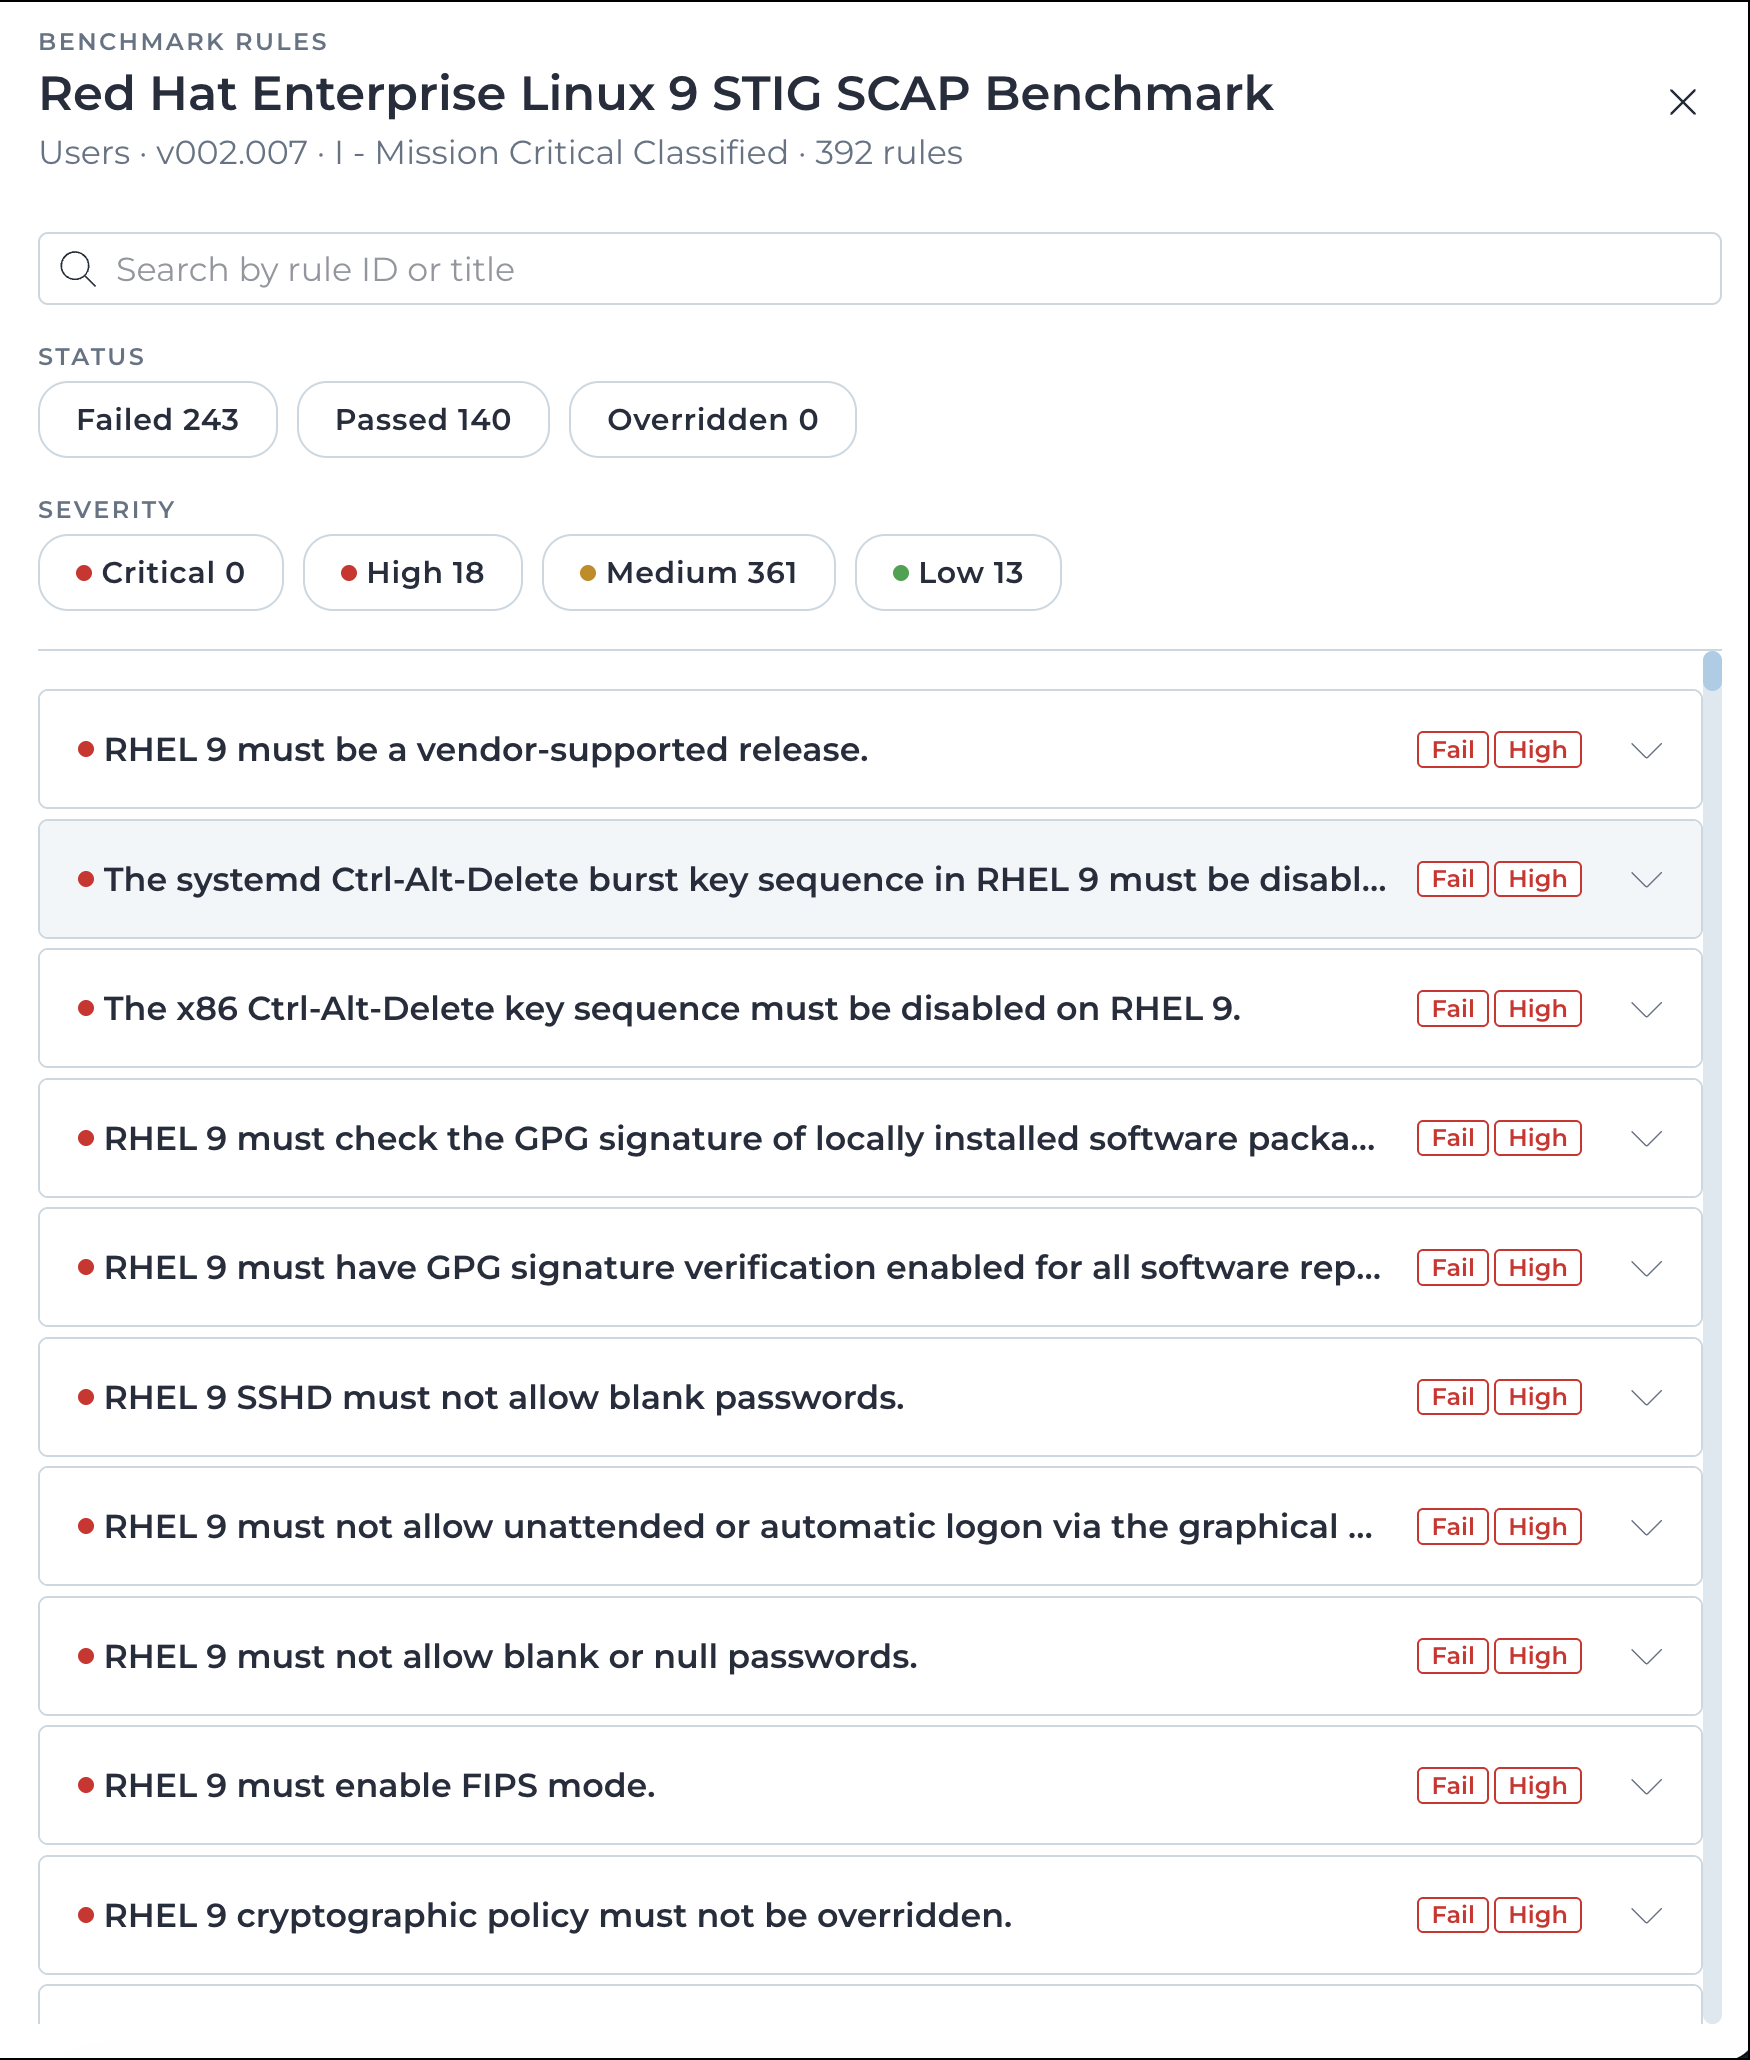 The rule list shows each rule's result, for example Pass or
Fail, and its severity. Filter the list by status or
severity: each option shows its own rule count, for example
Failed 243 or High 18. Select more
than one option within a group to combine them, or deselect all to show every rule.
You can also search by rule ID or title.