
Configure Fortinet FortiGate
Configure Guardian firewall integration with the Fortinet FortiGate firewall.
Before you begin
- You have administrator privileges
- You have generated the REST application programming interface (API) access token from the firewall admin Web user interface (UI)
- You have added the Guardian address subnet to trusted hostsNote:The access token needs to have permission to insert, read, and delete entities such as:
- Addresses
- Addrgroups
- Routes
- Sessions
- Policies
About this task
Guardian integration supports FortiOS versions 6.2, 6.4, 7.0, 7.2, and 7.4.9. This integration uses the REST API.
Procedure
-
In the top navigation bar, select
 The administration page opens.
-
In the Settings section, select Firewall
integration.
The Firewall integration page opens.
-
In the top right section, select +
A dialog shows.
-
From the Choose firewall dropdown, select
Fortinet FortiGate.
A dialog shows.
-
If it is not populated already, in the Host (CA-Emitted TLS
Certificate) field, enter the host internet protocol (IP) address.
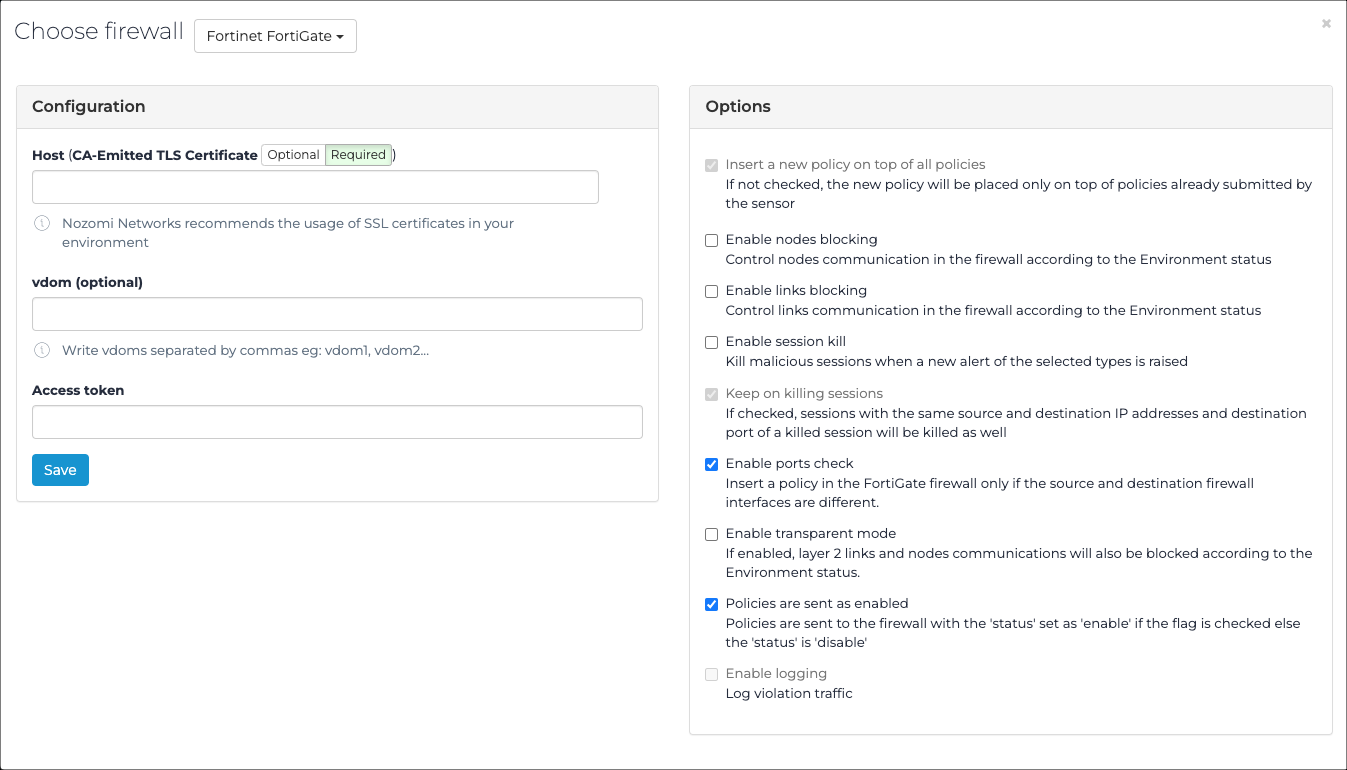
- Optional: In the vdom (optional) field, enter one or more Virtual DOM (vdom)s. Use a comma to separate multiple entries.
- In the Access token field, enter the access token.
- Optional:
If necessary, in the Options section, select one or more
of these options:
-
For Firewall rules strategy, select a strategy.
Figure 1. Firewall rules strategy toggle 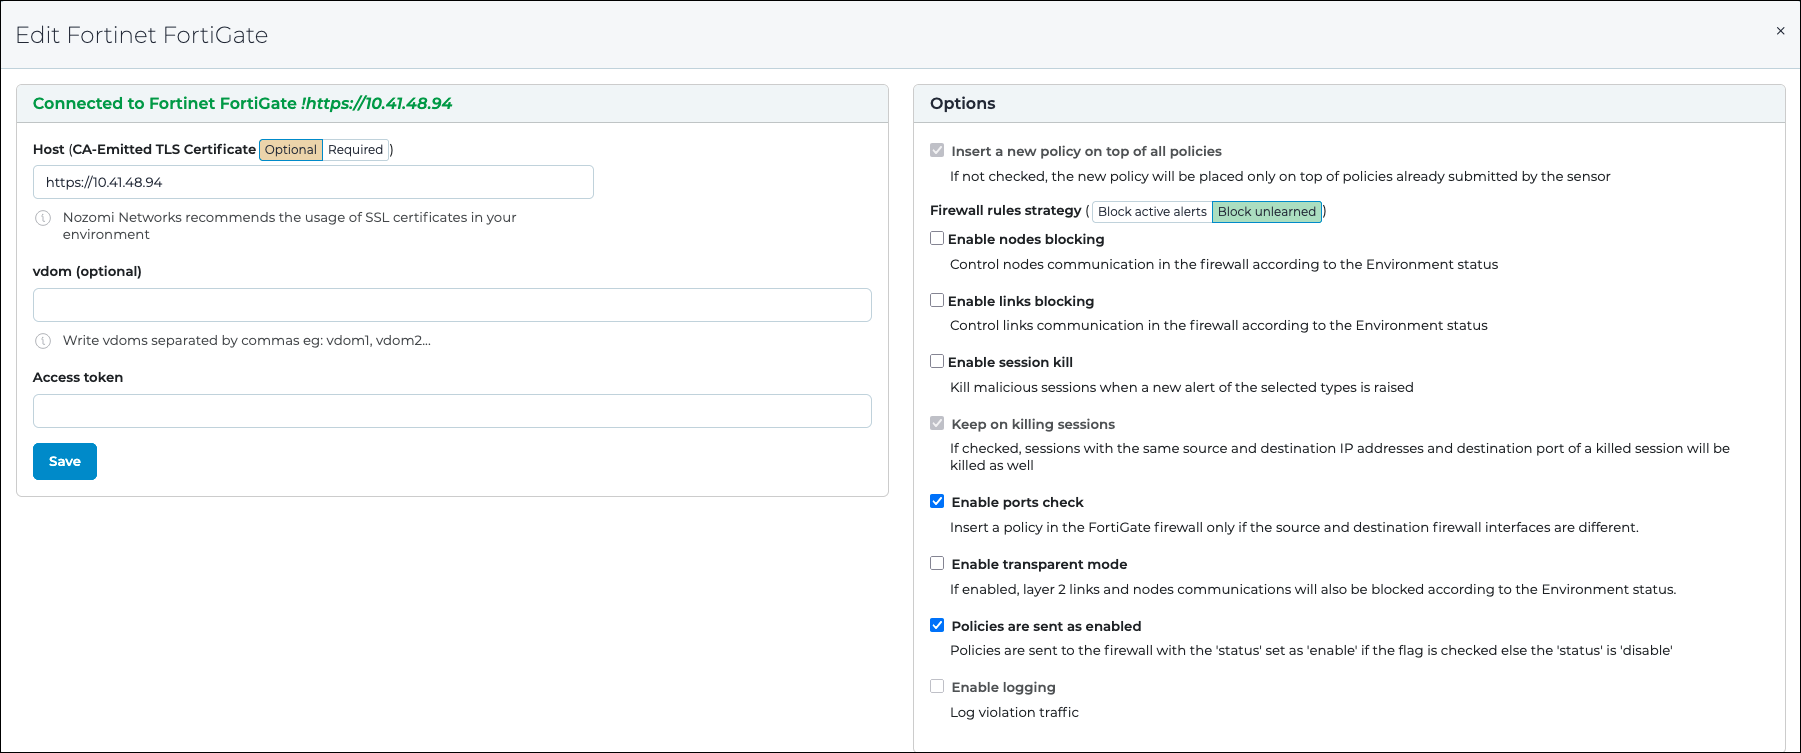
- Block active alerts: Guardian creates link-blocking policies when specific alerts are triggered. Guardian generates rules based on real-time detection events, not on node learning state. For more details, see Alert-based firewall rule creation.
- Block unlearned: Guardian creates block policies for unlearned nodes and links. This is the default behavior.
If you selected Block active alerts, select one or more alert types that should trigger firewall rule creation:
SIGN:MITMSIGN:SCADA-INJECTIONSIGN:PACKET-RULESIGN:OUTBOUND-CONNECTIONSSIGN:MALWARE-DETECTEDSIGN:MULTIPLE-ACCESS-DENIEDSIGN:MULTIPLE-UNSUCCESSFUL-LOGINSSIGN:NETWORK-SCAN
If
SIGN:PACKET-RULEis selected, enter a Severity threshold value and a Risk threshold value. Guardian creates a firewall rule forSIGN:PACKET-RULEalerts only when both the alert severity and the risk score meet or exceed the configured thresholds.
-
For Firewall rules strategy, select a strategy.
- Select Save.